CSG
ESTABLISHING SECURE GATEWAY
CSG CYBER DEFENSE EDUCATION & RESEARCH FOUNDATION
CSG CYBER DEFENSE EDUCATION & RESEARCH FOUNDATION
Executed full-scope stealth adversary emulation against a high-frequency trading platform and core transaction ledger, uncovering 3 zero-day memory corruptions.
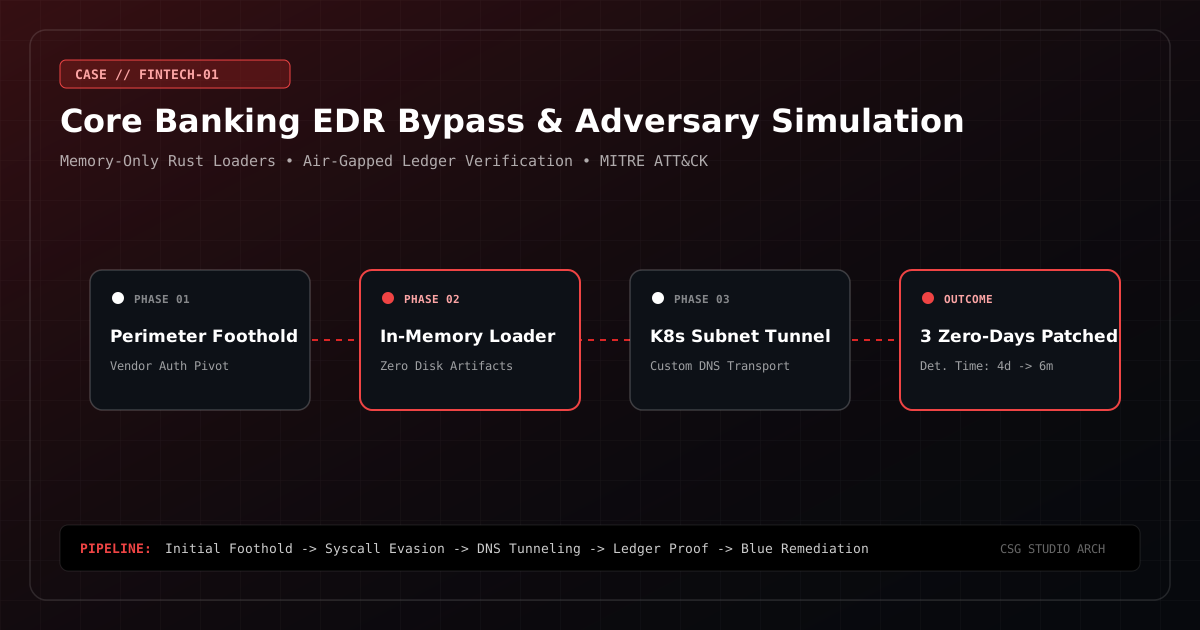
The client operated an air-gapped banking network protected by top-tier EDR solutions, strict zero-trust network access, and micro-segmented Kubernetes clusters. They needed to test whether a compromised third-party vendor credential could result in core ledger manipulation.
CSG Studio engineered custom in-memory loaders in Rust that bypassed user-mode API hooking. We simulated an in-memory credential harvesting campaign, pivoted across segmented subnets using custom TCP tunneling over DNS, and reached the ledger orchestration cluster.
Phase 1: Threat Modeling & Rules-of-Engagement Formalization
Phase 2: Custom Syscall Evasion Loader Development in Rust
Phase 3: Stealth Lateral Movement & DNS Tunneling Verification
Phase 4: Joint Purple Team Telemetry Replay & SIEM Rule Hardening
ARCHITECTUREVerified covert pivot across segmented VLANs to core ledger cluster.
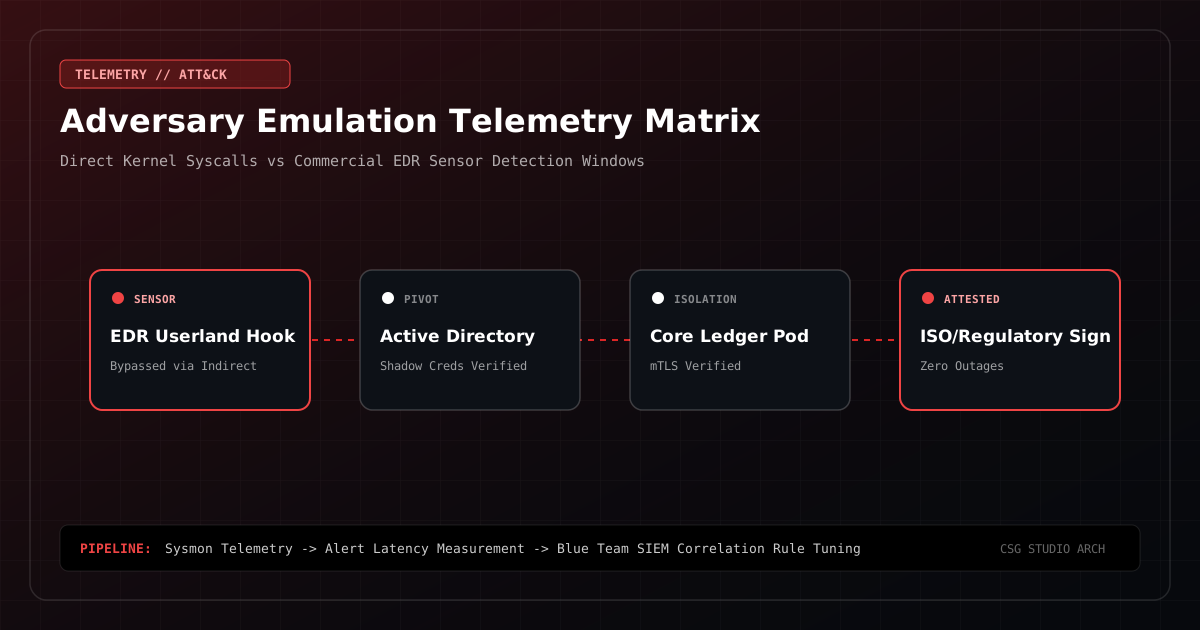 TELEMETRY
Telemetry gap telemetry timeline before vs after Blue Team rule hardening.
“CSG Studio delivered the most technically rigorous adversary emulation our institution has ever commissioned. Their team demonstrated how an attacker could bypass our multi-million dollar defensive stack, and then worked shoulder-to-shoulder with our engineers to remediate every vector. Unmatched technical depth.”
Comprehensive cloud boundary penetration test and IAM entitlement analysis.
Hardened regional substation telemetry protocols and engineered real-time DPI protocol dissectors to detect anomalous actuator manipulation.
Architected a specialized, air-gapped cyber range and synthetic command-and-control emulation platform for embedded avionics testing.
Transmit your scope brief directly to CSG Studio’s principal engineers. Reference case study apex-financial-core-audit and receive a tailored roadmap within 24 business hours.