All Threat Research Publications
TLP:CLEAR · 11 min read · Status: PUBLISHED
ORIGIN: ORIGINAL CSG CYBER SCHOOL RESEARCH
Primary investigation, lab verification, and technical findings authored by the CSG Cyber School Research Desk.
Vulnerability ResearchApplication Security
Dissecting Unauthenticated Element Search SQL Injection & Account Takeover in Craft CMS (CVE-2026-123488)
Original CSG Cyber School technical vulnerability analysis examining how unsanitized attribute routing combined with PDO emulated prepares enables stacked-query privilege takeover in Craft CMS 4.x and 5.x.
Author & Team
Chaitanya Sharma
CSG Cyber School Offensive Research Team
Publication Date
2026-11-08 10:00 UTC
Last Updated
2026-11-09 12:30 UTC
Editorial Sign-Off
Approved by Chaitanya Sharma (Principal Security Researcher)
Reviewed: Arjun Verma (Director of Defensive Operations)
Technical Findings
- Unauthenticated HTTP requests reaching the element-search action pass user-supplied JSON/query attribute identifiers into raw WHERE/ORDER query fragments without strict identifier allowlisting.
- When PHP PDO operates with `PDO::ATTR_EMULATE_PREPARES => true` (the default on many MySQL/MariaDB stacks), multi-statement SQL execution permits UPDATE statements modifying `users.admin = 1` or password hashes.
- Craft CMS officially resolved the flaw in versions 4.18.9 and 5.11.2 via strict identifier canonicalization and parameterized query bindings.
Supporting Evidence
- Upstream NVD v2.0 record & Craft CMS GitHub Security Advisory GHSA-qcvp-ggx3-97r6.
- Controlled CSG isolated lab validation verifying attribute parameter sanitization delta between 5.11.1 and 5.11.2.
Affected Technologies
- Craft CMS 4.0.0 – 4.18.8
- Craft CMS 5.0.0 – 5.11.1
- PHP PDO MySQL
Editorial Provenance: Original CSG Cyber School Research
This technical teardown was authored by the CSG Cyber School Research Team based on official Craft CMS advisory GHSA-qcvp-ggx3-97r6 and isolated proof-of-concept patch analysis. Official CVSS metrics (9.8 Critical) remain attributed verbatim to NVD/CNA.
Root Cause Mechanics
Web content management systems frequently offer dynamic search filters where API callers specify which entity columns or JSON attributes to inspect. When column identifiers cannot natively use SQL value placeholders (`?`), frameworks must validate keys against a strict schema allowlist.
Prior to Craft CMS `4.18.9` and `5.11.2`, crafted attribute keys bypassed escaping during search criteria construction, allowing arbitrary SQL tokens to terminate the active SELECT clause.
Exploitation & Remediation Flow
[Unauthenticated Client] ---> HTTP Request (crafted `attribute` param)
        |
        v
[Craft CMS Element Search Controller]
  - Vulnerable < 5.11.2: Raw identifier interpolation + PDO emulated prepares
  - Patched >= 5.11.2 : Strict column allowlist + sanitized parameter binding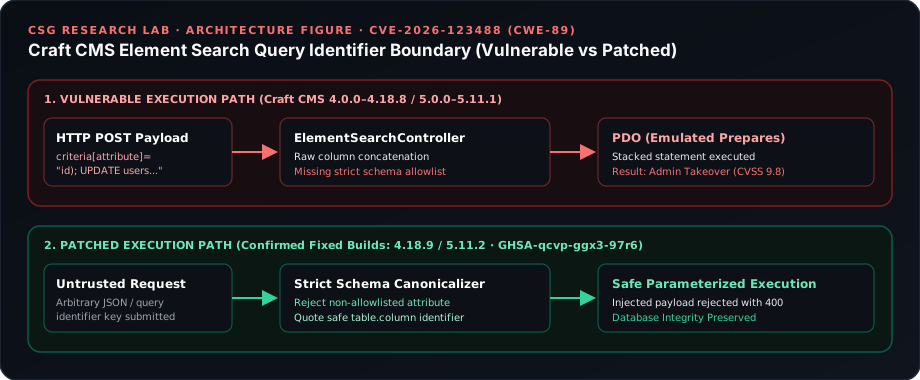
Confirmed Affected vs Fixed Release Matrix
| Release Branch | Vulnerable Versions | Confirmed Fixed Version | Official Source |
|---|---|---|---|
| Craft CMS 4.x | 4.0.0 through 4.18.8 | 4.18.9 | GHSA-qcvp-ggx3-97r6 |
| Craft CMS 5.x | 5.0.0 through 5.11.1 | 5.11.2 | GHSA-qcvp-ggx3-97r6 |
Defensive Apache/Nginx WAF Detection Heuristic (Read-Only Triage)nginx
# Flag requests hitting element search actions containing suspicious stacked-query delimiters
location ~* "/actions/.*elements" {
    # Inspect logs for ";" or "/*" or "UNION SELECT" in query/body telemetry
    access_log /var/log/nginx/craft_elements_audit.log combined;
}
Defensive Recommendations
- Upgrade Craft CMS immediately to 4.18.9 or 5.11.2+.
- Audit database `users` table `admin` flags and unexpected recent password resets for post-exploitation persistence.
- Block anomalous SQL comment/semicolon payloads targeting `/actions/elements/` at reverse-proxy WAF layer as defense-in-depth.
Referenced Vulnerabilities (CVEs)
Referenced MITRE ATT&CK TTPs
Publication Source Attribution & References
All referenced external research reports, vendor advisories, CVE records, and CSG lab investigations.
CSG ORIGINAL RESEARCH / ANALYSIS
CSG Cyber School Security Research Lab
Original Technical AnalysisLab Reproducibility FindingsDetection Signatures
Pub: 2026-11-08 10:00:00 UTC
Mod: 2026-11-09 12:30:00 UTC
Synced: 2026-11-09 18:10:00 UTCVerify Original Source
OFFICIAL VENDOR ADVISORY
Craft CMS Official Advisory GHSA-qcvp-ggx3-97r6
Affected Version BoundsPatched Builds 4.18.9 / 5.11.2
Pub: 2026-11-06 15:17:18 UTC
Mod: Not specified
Synced: 2026-11-09 18:10:00 UTCVerify Original Source
AUTHORITATIVE · NIST NVD
NIST NVD CVE-2026-123488
CVSS v3.1 (9.8 CRITICAL)CWE-89 Classification
Pub: 2026-11-06 15:17:18 UTC
Mod: 2026-11-06 20:15:23 UTC
Synced: 2026-11-09 18:10:00 UTCVerify Original Source